

Octagon Networks @OctagonNetworks
We are a global company made up of hackers and security researchers working together to tackle advanced vulnerabilities & techniques using AI. Building @pwn_ai octagon.net New York, USA Joined June 2025-
Tweets102
-
Followers168
-
Following1
-
Likes407

Full VM escape zeroday (guest>host root in industry standard hypervisors)! More soon
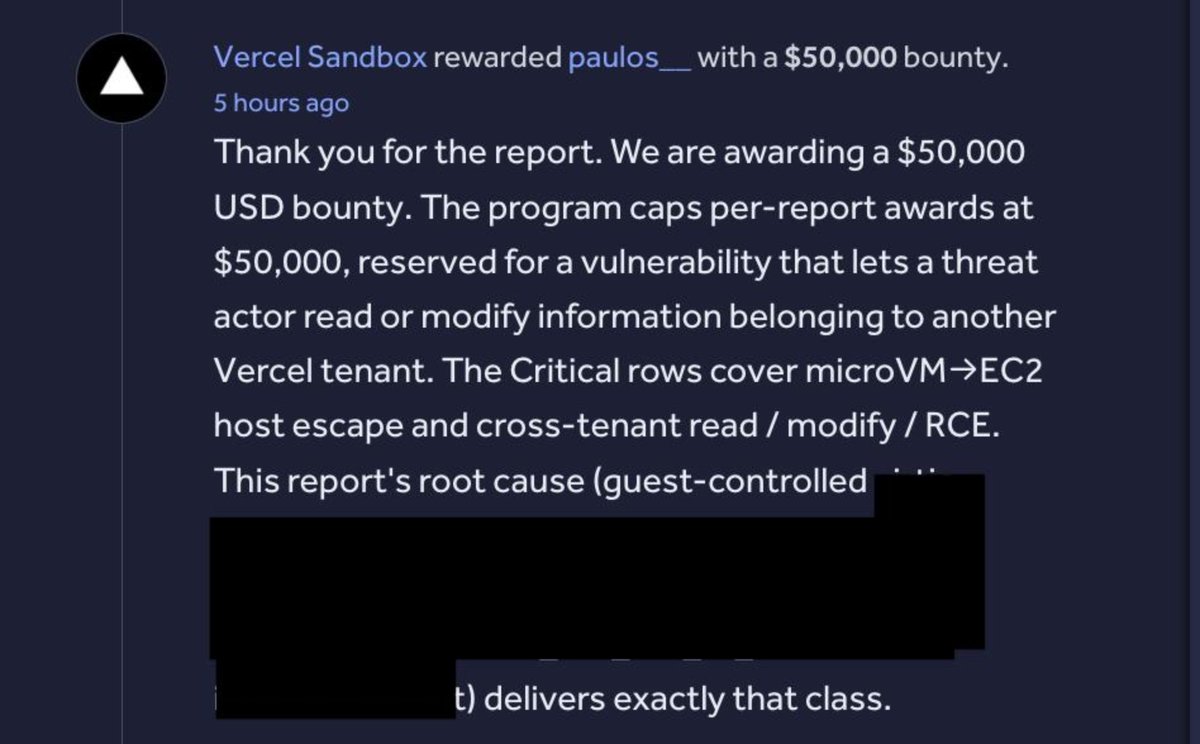

A lot of speculation on if KVM bugs have gotten cheaper, and why id do it for 50k instead of a milly. I wasn't born yesterday. I know I couldve sold it for waayy more. I didnt want to. I did it for the love of the game. I wanted to know if I could do it, and now we know i can.
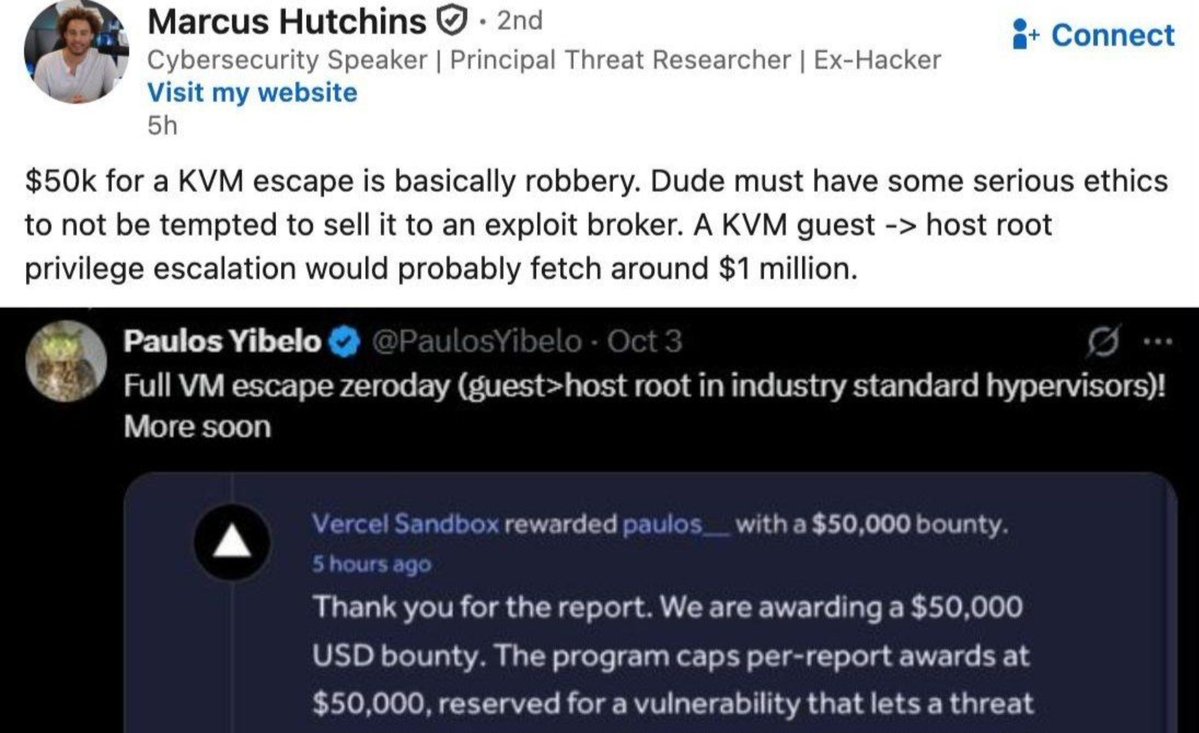
A lot of speculation on if KVM bugs have gotten cheaper, and why id do it for 50k instead of a milly. I wasn't born yesterday. I know I couldve sold it for waayy more. I didnt want to. I did it for the love of the game. I wanted to know if I could do it, and now we know i can. Maybe I am a big dreamer?
Vercel is the best security team we have worked with. The entire management chain is hyper paranoid and wonderful to work with! We will release more on these container escapes once the patches land! Stay tuned!
We’ve confirmed a KVM 0day through our Vercel Sandbox bounty program. Affecting the industry’s gold standard solution for Linux virtualization. 2026 is wild! Thankful to Paulos and other researchers helping us make the most secure sandbox for agents. Full writeup coming.
Containers don't contain, but VMs don't contain either :-)
Full VM escape zeroday (guest>host root in industry standard hypervisors)! More soon
@S1r1u5_ We think the operators intution is still everything that decides quality. Seems like a very rare combo
KVM has a zero day in it. That's the hypervisor underneath nearly every AI agent sandbox on the market, found through Vercel's own bug bounty program. Paulos Yibelo reported a full VM escape, guest to host root, in what Guillermo Rauch called the industry's gold standard for Linux virtualization. The specific finding that paid out at the program's $50,000 critical tier was a cross-tenant read, modify, and remote code execution path from microVM to host. That's not a Vercel bug. That's a bug in the thing underneath Vercel, and underneath most of its competitors too. Worth sitting with the market this sits inside. E2B is valued around $104 million, Daytona just raised a $24 million Series A at roughly $125 million, and Modal is reportedly in talks to raise $750 million at a $16 billion valuation, triple what it was in May, on revenue that went from $60 million to $300 million in eight months after launching over a billion sandbox instances. Everyone in this category competes on cold start time and price per vCPU hour. A recent benchmark put Vercel at 0.67 seconds median time to interactive against Daytona's 0.27, though Daytona's success rate under burst load was only 37%, which tells you a median alone doesn't mean much. Per thousand executions under a realistic idle heavy agent pattern, Northflank priced out near $11 and Modal near $40. Here's what none of that pricing table captures. E2B and Vercel resolve a conflicting allow list and deny list in opposite directions, so the same IP rule produces a different security outcome depending on which provider you picked for the speed numbers. Almost nobody shops for a sandbox on that detail, until an agent running untrusted code all day finds the one network path or kernel path the model didn't account for. That's exactly what happened here. The whole category sells isolation as a commodity feature with a price tag attached. A $50,000 bounty payout is a reminder that the isolation is a shared, rented foundation with one landlord, the Linux kernel, and every tenant's security posture is only as good as how hard that landlord has actually been tested. x.com/rauchg/status/…
We’ve confirmed a KVM 0day through our Vercel Sandbox bounty program. Affecting the industry’s gold standard solution for Linux virtualization. 2026 is wild! Thankful to Paulos and other researchers helping us make the most secure sandbox for agents. Full writeup coming.

btw, this is quite huge. there is no sandbox from any provider today that i would treat as unescapable by a sufficiently capable adversarial agent. containers fell. kvm fell. sandboxing is hard!!!
Full VM escape zeroday (guest>host root in industry standard hypervisors)! More soon
.@DarioAmodei and @sama! it is high time you put some money into KYC, or whatever trust/verification system you want, and give legitimate security researchers access to your best models. 1. we’ve helped secure both of your companies multiple times against issues that could have had serious consequences. i wouldn’t be surprised if we can keep doing that, and i also wouldn’t assume every capable attacker is reporting what they find. 2. there is now a KVM escape that, if researchers hadn’t found it first, could have been exactly the kind of thing your models eventually find in another hugging face style incident. you know, the list will keep growing, this is not the end. it rationally makes sense to get as many trusted researchers and companies as possible red teaming your companies, your models, and the infrastructure they depend on.
Nice. This year is the year of the VM escape. But I read the kvm ML and tree daily, and nothing in the recent public kvm patches looks like a microvm escape. Probably not "kvm" but another virt stack. Maybe I missed it, or a stealth merge is coming. Curious either way.
We’ve confirmed a KVM 0day through our Vercel Sandbox bounty program. Affecting the industry’s gold standard solution for Linux virtualization. 2026 is wild! Thankful to Paulos and other researchers helping us make the most secure sandbox for agents. Full writeup coming.
Guest-host escapes are the nightmare virtualization scenario. If true, observers have suggested the potential seriousness of the flaw means this researcher's reward should be more than the $50k max under the bug bounty program. Read more here: theregister.com/offbeat/2026/1…

Type of hunters you see at the BBP after you announce a $1m bounty

Absolute madness of a finding and justice for Paulos because the bounty is a tiny fraction of what he deserves. Congrats buddy!
Full VM escape zeroday (guest>host root in industry standard hypervisors)! More soon

Wait. Look at @rauchg avatar. Is he fondling @PaulosYibelo??!?!
🗞️ @rauchg followed @PaulosYibelo @PaulosYibelo reported a virtual-machine escape this week, with @vercel confirming a KVM zero-day through its sandbox bounty program and a full write-up still to come.

Sandboxing is more important than ever. Exactly why we put a $200k bounty on a Firecracker/gVisor escape on ZeroDay.Cloud/2026
We’ve confirmed a KVM 0day through our Vercel Sandbox bounty program. Affecting the industry’s gold standard solution for Linux virtualization. 2026 is wild! Thankful to Paulos and other researchers helping us make the most secure sandbox for agents. Full writeup coming.
next-level detection & response 😅 > half-jokingly suggested trying to rediscover the bug > set up the environment, started an agent with a cyber model, gave it one clue partway through (not saying what it was until the patch is out :))) > ~2 hours later: found the bug and validated an end-to-end exploit* > …** hats off to @PaulosYibelo for the original discovery… incredible work! definitely not an easy bug to find, especially without “cheating” :D * x.com/0x4d31/status/… ** x.com/zbraniecki/sta…
i probably won’t sleep until i rediscover this with my agent :)) and i’m not even a vuln researcher…!

Funnily enough, I broadly agree with Mr. @DeGatchi. For vulnerabilities like this one which impacts everybody using KVM (read every hyperscaler, every AI lab, every company on the planet really), there should be a fund that pays from all of them. As Vercel we are trying to do our part here. And all credit to @PaulosYibelo for going down the pass of responsible disclosure!

This is a great idea, and I hope it applies
Funnily enough, I broadly agree with Mr. @DeGatchi. For vulnerabilities like this one which impacts everybody using KVM (read every hyperscaler, every AI lab, every company on the planet really), there should be a fund that pays from all of them. As Vercel we are trying to do
This idea could geniuley transform bug bounty and really align incentives of most researchers and hackers, as well as help the internet find the nastiest bugs really quickly. This is a top tier CTO comment and if done, I have no doubt it would start a security revolution! So many talented hackers don't even look bc reporting etc is just a mess, or often just unrecognized so god knows what's buried in random dependacies of the everyday tools we use. 1000% agree
Funnily enough, I broadly agree with Mr. @DeGatchi. For vulnerabilities like this one which impacts everybody using KVM (read every hyperscaler, every AI lab, every company on the planet really), there should be a fund that pays from all of them. As Vercel we are trying to do

D @deusgrana
2 Followers 22 Following
manu.miglioranza @bigboss_14180
34 Followers 1K Following A ver si en esta cuenta el algoritmo para de banearme un poco. Software development Mes opinions m'appartiennent
yonas jemberu @yon80798
1 Followers 103 Following Backend Engineer | Laravel | APIs | Systems Building scalable systems Sharing real backend engineering lessons

Hen @defibrah88
147 Followers 1K Following professional noob; on the journey to somewhere and nowhere
Keven Belanger @KevenBelanger
437 Followers 5K Following Single Father of 3 – Asperger – 🇺🇸 🇫🇷 🇮🇹 IT / Cybersecurity / Forensics / OSINT


Lucas Skywalker @fariavalue
155 Followers 2K Following technoOPTIMIST | pre-med dropout • hacking | live by the 3C’s: curiosity, creativity and courage. 🇧🇷🇺🇸

pwn.ai @pwn_ai
13K Followers 3 Following Built to breach. The best defense is insane offense. we escape sandboxes & hack everything. Agentic hacking ecosystem in the works. pentest product is now live
Alex Rad @defendtheworld
2K Followers 2K Following On a mission to make networking secure and simple. https://t.co/NnoAMwpuYA
Daniel Kumanaya @DanielKumanaya
371 Followers 2K Following Developer. Builder. Occasionally shipping weird ideas.


N𝔸𝕍ⒺεŇ @Asympt0t3
77 Followers 2K Following 73 110 102 111 115 101 99 32 71 117 121 | 𝕋𝕙𝕖 ℂ𝕦𝕣𝕖 𝕗𝕠𝕣 𝔹𝕠𝕣𝕖𝕕𝕠𝕞 𝕀𝕤 ℂ𝕦𝕣𝕚𝕠𝕤𝕚𝕥𝕪. 𝕋𝕙𝕖𝕣𝕖 𝕀𝕤 ℕ𝕠 ℂ𝕦𝕣𝕖 𝕗𝕠𝕣 ℂ𝕦𝕣𝕚𝕠𝕤𝕚𝕥𝕪.🙂
tmajik @tmajik2235
2 Followers 326 Following

Cailloux @Cailloux968499
24 Followers 3K Following

Aurélien Zogbah @SZogbah
1K Followers 2K Following Bridging nature and science 🌍 | Real Madrid 🇪🇸| 🎵 influencer | GodOnDuty🙏💯|

android_ios_chrome @ChromeIos97000
0 Followers 299 Following
its me @itsme5cn
0 Followers 32 Following
Sai Ashwin @hsaias_
62 Followers 4K Following undergrad @iitmadras. tech lead @RaftarIITM. security research @iitmcse. ambition/skill approaching infinity. professional token user
samee @sameehnph
5 Followers 137 Following

Younes @younesfdj
165 Followers 121 Following 22 | Software engineer Backend and DevOps enthusiast . . Trying to build something useful


larmelli @lelloarmelli
57 Followers 334 Following
Dan @DanIskandarov
25 Followers 4K Following

Himanshu Singh @hk755a2
6 Followers 726 Following
Rebellions Are Built ... @Self_HelpJunkie
2K Followers 7K Following To all future trolls: I am a Ron & Rand Paul, Thomas Massie minded person. I believe in… personal FREEDOM… FREE markets… FREE exchange of ideas


x8bitranjit @x8bitranjit
23 Followers 217 Following "It's not who I am underneath, but what I do that defines me. "
Satochiche @satochiche
880 Followers 5K Following
Sarfrazz @Sarfraz_Hulio
135 Followers 3K Following

Raymond @raymondlsfs
0 Followers 6K Following

Nati @NatiTekle96
5 Followers 125 Following
Malcolm X0r @AccordingToMark
556 Followers 8K Following What’s in my cup is in my cup, fuck you! - Lil’ Wayne.
pwn.ai @pwn_ai
13K Followers 3 Following Built to breach. The best defense is insane offense. we escape sandboxes & hack everything. Agentic hacking ecosystem in the works. pentest product is now liveYou might like


















