Monpulse @monpulsealert
Joined October 2025-
Tweets106
-
Followers1
-
Following219
-
Likes113

🚨 İddiaya göre bir güvenlik araştırmacısı, CrowdStrike, SentinelOne, Cortex XDR ve Sophos'un tespit mekanizmalarını tersine mühendislikle yeniden oluşturdu. Bu sayede dosyaların VirusTotal'e yüklenmeden, tamamen çevrimdışı ortamda bu EDR çözümlerine yakalanıp yakalanmayacağı test edilebiliyor. Bu gelişme hem güvenlik araştırmacılarının hem de maalesef saldırganlar açısından dikkat çekici. İddia eğer doğruysa, siber saldırganların, kendi zararlı yazılımlarını EDR'lere yakalanmadan önce test edip, optimize etmesine neden olabilir.


🚨 GRAVE: Bug en FreeBSD de 7 años afectó Netflix CDN, PlayStation OS y WhatsApp. Descubierto recién el año pasado, este exploit tenía un impacto masivo en infraestructuras críticas. Impresionante cómo pasó desapercibido tanto tiempo #FreeBSD #cybersecur…

software engineering in 2026: - your package manager is compromised - your cloud provider blocks your account - github itself is hacked software is solved
Uuu, grubiutko. GitHub zhackowany. Zaczęło się od pracownika który zainstalował zainfekowany dodatek do VS Code. Wykradziono kod wewnętrznych repozytoriów. Dane są aktualnie sprzedawane przez grupę teamPCP. W wielu firmach programiści są - tak samo jak w Githubie - już dawno trzaśnięci..Tylko jeszcze o tym nie wiedzą.


🚨Data Breach Alert ‼️ 𝗧𝗲𝗮𝗺𝗣𝗖𝗣 𝗖𝗹𝗮𝗶𝗺𝘀 𝗦𝗮𝗹𝗲 𝗼𝗳 𝗚𝗶𝘁𝗛𝘂𝗯 𝗜𝗻𝘁𝗲𝗿𝗻𝗮𝗹 𝗦𝗼𝘂𝗿𝗰𝗲 𝗖𝗼𝗱𝗲 TeamPCP hacking group claimed the compromise and sale of GitHub internal data, allegedly including around 4,000 private repositories containing source code related to GitHub’s main platform and internal organizations. Threat actor: TeamPCP Sector: ICT Data exposure (claimed): Approximately 4,000 private repositories Data type: Source code Observed: May 19, 2026 Status: Pending verification ESIX©: 7.96 Full details and impact assessment on HackRisk.io


‼️🚨 The Mini Shai-Hulud npm worm has hit again. Hundreds of antv packages compromised (Alibaba's data visualization suite) along with echarts-for-react, timeago.js, size-sensor, and canvas-nest.js. It all started today with the compromise of npm account atool ([email protected]). In a 22-minute window between 01:39 and 02:06 UTC, the attacker published 631 malicious versions across 314 packages, all carrying the same payload. Top affected packages by monthly downloads: - [email protected] - 4.2M dl/mo - [email protected] - 3.8M dl/mo - @antv/[email protected] - 2.2M dl/mo - [email protected] - 1.15M dl/mo - @antv/[email protected] - 1.0M dl/mo - @antv/[email protected] - 1.1M dl/mo - @antv/[email protected] - 975K dl/mo - @antv/[email protected] - 883K dl/mo - @antv/[email protected] - 751K dl/mo What the payload does (498KB obfuscated Bun script, runs via preinstall hook): - Harvests 20+ secret types: GitHub PATs, npm tokens, AWS keys, GCP service accounts, Azure creds, DB connection strings, Stripe keys, Slack tokens, SSH keys, Docker auth, Kubernetes configs, Vault tokens - Attempts Docker container escape if the host socket is reachable, spinning up a Privileged container with host filesystem bind mounts - Pulls a secondary payload via optional dependency antv/setup from antvis/G2 commit 1916faa, which was pushed 19 minutes before the npm publishes started


🚨 فيديو إثبات (PoC) يُظهر استغلال ثغرة جديدة باسم "YellowKey" تتجاوز حماية BitLocker كاملةً على نظام Windows. 🔹 الفيديو يوضّح خطوة بخطوة طريقة الاستغلال: 1- نسخ مجلد FsTx إلى ذاكرة USB 2- الدخول إلى وضع Windows Recovery Environment 3- تنفيذ تركيبة مفاتيح (SHIFT + CTRL) للحصول على Shell بصلاحيات كاملة على القرص المشفّر دون الحاجة لكلمة مرور أو مفتاح استرداد Credit: @DarkWebInformer

🇫🇷 An underground platform called “ARGUS LOOKUP/SPYWARE” is being advertised as a French doxxing, geolocation, and surveillance-style intelligence tool allegedly aggregating data from multiple sources in real time. The interface shown in the underground advertisement appears to include capabilities such as: • identity lookup • phone and email correlation • geolocation tracking • facial recognition • dossier creation • IP intelligence • historical activity analysis • social and financial correlation mapping The post also references alleged access to multiple French-related data sources and administrative-style datasets. At this stage, the legitimacy, functionality, and actual access level of the platform remain unverified. However, platforms marketed as “lookup” or “spyware” ecosystems often combine: • leaked databases • scraped information • OSINT aggregation • credential dumps • telecom metadata • social engineering tools • and doxxing-focused analytics Even when exaggerated, these types of services can significantly increase risks related to: • privacy violations • stalking and harassment • doxxing campaigns • identity theft • extortion • targeted surveillance • and criminal intelligence gathering The commercialization of real-time identity correlation and geolocation tooling continues to blur the line between cybercrime, spyware ecosystems, and underground intelligence-as-a-service operations. Daily Dark Web is continuing to monitor the situation. #France #French #CyberSecurity #Spyware #Doxxing #ThreatIntelligence #DDW #Intelligence


🪟 New Windows challenge: JanelaRAT Reverse a real-world RAT, from the initial dropper down to the final C2. 📦 Installer triage 🔍 17 questions 🧬 Multi-stage unpacking 🔐 Config decryption 🌐 C2 hunting 🔗 malops.io/challenges/jan… 💬 discord.gg/PHRd7xPUUt By @P4nd3m1cb0y


Acaba de confirmarse: Un exploit de zero-day llamado 'MiniPlasma' permite a los atacantes obtener acceso de SYSTEM en sistemas Windows completamente actualizados. El exploit afecta a Microsoft Windows, específicamente al servicio de impresión y manejo de colas de impresión, y permite una elevación de privilegios locales (LPE) a NT AUTHORITY\SYSTEM. La vulnerabilidad es de tipo zero-day, sin parche oficial disponible, y se ha publicado un proof-of-concept (PoC) que demuestra su explotación en sistemas Windows totalmente parcheados. El impacto es grave, ya que permite a los atacantes obtener acceso de SYSTEM a los sistemas afectados, lo que podría llevar a daños. ¿Hay parche? No, por ahora. ¿Qué deben hacer los afectados HOY? Revisar los logs de seguridad y monitorear el sistema para detectar cualquier actividad sospechosa. ¿Estás en riesgo? Revisa esto: actualiza tus sistemas lo antes posible y aplica las medidas de seguridad recomendadas. bleepingcomputer.com/news/microsoft…
🚨 Microsoft hesaplarını hedef alan yeni bir siber tehdit dalgası tespit edildi. Saldırganlar, Microsoft’un “şifresiz giriş” özelliğini kötüye kullanarak sızdırılmış e-posta veritabanlarıyla hesap keşfi yapıyor linkedin.com/posts/sibergae…

RDP Stealer with Windows Defender Bypass

GitHub - friparia/NGINX_RIFT_SCAN_CVE_2026_42945: Scan Nginx Rift (CVE-2026-42945) · GitHub github.com/friparia/NGINX…

谷歌不想让你知道的50个网站 1. '12ft.io' — 绕过任何付费墙 2. 'libgen.is' — 数百万免费教科书 3. 'sci-hub.se' — 免费研究论文 4. 'alternativeto.net' — 寻找免费应用替代品 5. 'justwatch.com' — 找到任何内容的流媒体位置 6. 'archive.org' — 访问任何旧网页 7. 'gutenberg.org' — 7万本免费经典书籍 8. 'pdfdrive.com' — 免费PDF下载 9. 'openculture.com' — 顶级大学免费课程 10. 'wolframalpha.com' — 即时求解任何数学题 11. 'photopea.com' — 浏览器内免费Photoshop 12. 'squoosh.app' — 免费压缩任何图像 13. 'remove.bg' — 免费移除图像背景 14. 'cleanup.pictures' — 从照片中擦除物体 15. 'unscreen.com' — 移除视频背景 16. 'carbon.now.sh' — 将代码转换为艺术 17. 'ray.so' — 精美代码截图 18. 'shots.so' — 免费产品模型 19. 'smartmockups.com' — 无需Photoshop的模型 20. 'haveibeenpwned.com' — 检查您是否被黑客攻击 21. 'virustotal.com' — 扫描任何文件中的恶意软件 22. 'privnote.com' — 发送自毁消息 23. 'temp-mail.org' — 即时一次性邮箱 24. 'file.io' — 共享自动删除的文件 25. 'archive.ph' — 永久保存任何网页 26. 'similarsites.com' — 寻找任何网站的替代品 27. 'radio.garden' — 收听全球任何电台 28. 'everynoise.com' — 探索每种音乐流派 29. 'tunefind.com' — 从任何剧集查找歌曲 30. 'musicforprogramming.net' — 专注音乐 31. 'mynoise.net' — 自定义专注声景 32. 'coffitivity.com' — 咖啡厅声音促进生产力 33. 'elicit.org' — AI研究论文助手 34. 'consensus.app' — 搜索科学共识 35. 'connectedpapers.com' — 可视化研究地图 36. 'semanticscholar.org' — 免费学术搜索 37. 'scispace.com' — 理解任何研究论文 38. 'summarize.tech' — 总结任何YouTube视频 39. 'phind.com' — 开发者AI搜索 40. 'regex101.com' — 即时测试任何正则表达式 41. 'codebeautify.org' — 整洁格式化代码 42. 'jsonformatter.org' — 像人类一样读JSON 43. 'explainshell.com' — 理解终端命令 44. 'raindrop.io' — 有效的书签管理器 45. 'downdetector.com' — 检查任何网站是否宕机 46. 'tineye.com' — 反向图像搜索 47. 'fast.com' — 检查网速 48. 'smallpdf.com' — 免费编辑PDF 49. 'ilovepdf.com' — 合并和分割PDF 50. '10minutemail.com' — 秒级临时邮箱 互联网远大于谷歌展示的内容。 大多数人永远不会离开第一页。


CVE-2026-44578: Next.js WebSocket Upgrade SSRF — pre-auth credential theft via localhost:80. Lab + exploit + audit. github.com/dinosn/CVE-202…
🚨Cyber Alert ‼️ 🇺🇸USA - 𝗚𝗿𝗮𝗳𝗮𝗻𝗮 Coinbase Cartel hacking group claims to have breached Grafana. Threat actor: Coinbase Cartel Sector: ICT Data exposure (claimed): Not specified Data type: Not specified Observed: May 15, 2026 Status: Pending verification ESIX©: 5.58 Full details and impact assessment on HackRisk.io

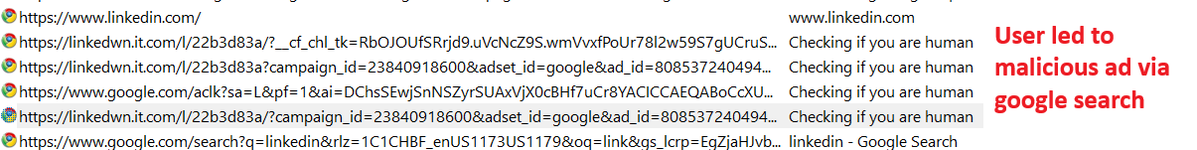
LinkedIn Search leads to #CastleLoader delivering #AsyncRAT. Attackers use Clickfix lures with fake verification popups to mask PowerShell activity. The loader decrypts the payload via RC4, using the first 64 bytes as a key to bypass filters. Details: bit.ly/4uOIqka


Nueva vulnerabilidad en #Linux que permite a usuarios locales sin privilegios leer archivos propiedad de root. Se llama ssh-keysign-pwn fue descubierta por Qualys ayer 14 de mayo pero ya fue corregida hoy por la mañana y está disponible para las distribuciones. lore.kernel.org/lkml/202605150…

Germany’s spy agency picks French AI firm over Palantir politico.eu/article/german…

Moftgate @moftgate
4 Followers 3 Following Endpoint Management RMM Data Loss Prevention SaaS Posture Management Data Governance AI Governance Exposure Management
Moftgate @moftgate
4 Followers 3 Following Endpoint Management RMM Data Loss Prevention SaaS Posture Management Data Governance AI Governance Exposure Management
ThreatCluster.io @threatcluster
589 Followers 626 Following Threat intelligence as data: a REST API, free IOC and MISP feeds and an MCP server. Over 20,000+ sources and ransomware leak sites.
CyberPulse @CyberPulse56
4K Followers 273 Following 🔎 OSINT-driven cybersecurity intelligence Breaches | Threat Actors | Malware | Phishing | CVEs | Dark Web Monitoring
HydrogenE7 @Hydrogen0E7
4K Followers 975 Following Full-Stack Security Developer | CTFer in @r3kapig | ACMer | Shotacon | Enchanting dream, frozen time, unrealized potential. Also @E7Lemon
deadc0de @0xdeadc0de___
276 Followers 280 Following Security R&D @ Quarkslab · Obsessed with RE & symbolic execution · Compilers lie. Obfuscators gaslight. Retired CTF Player
R1s @R1s666
1K Followers 263 Following 2024 2025 MSRC MVR / Web security / Bug Bounty / Web3 / Senior at Hanyang University
Andrea (Drego) Draghe... @AndreaDraghetti
7K Followers 3K Following aka Drego. Head of Cyber Threat Intelligence at @D3LabIT! @PhishingArmy, #meioc is my projects and @backbox_org dev! My passions are #F1 and #Running!

CyberA @CyberA94
5K Followers 184 Following Founder of SAFAR Mobile App | Cybersecurity|AI | DFIR ⚔️ Awareness & Digital Safety 🛡️ Authorized Use Only ⚖️| وَقُلْ رَبِّ زِدْنِي عِلْمًا

7h3h4ckv157 @7h3h4ckv157
57K Followers 99 Following Hacker | Hall of Fame: Google, Apple, X, NASA | BlackHat x1 | CVE ×4 | HTB SME (Guru) | BC: P1 warrior | Featured in NASA’s IT Talk | OSCP+ | Consultant at EY
Haluk Bayraktar @haluk
702K Followers 672 Following @BaykarTech CEO / @SahaIstanbul https://t.co/7FCtDXm9bR…
Nix0n @UnTalNixon_exe
5K Followers 2K Following 👨🏽💻 Cybersecurity | Web3 & Crypto Developer | AI Integrator @casaweb3
misaki @tdatwja
3K Followers 5K Following Cyber Security|APT|Attribution|infoOps|Geopolitics(China, DPRK)... 避難用アカウント: @_tdatwja
Raúl León @rleon_mx
7K Followers 5K Following Cybersecurity Specialist/ InfoSec Rockstar / Business Intelligence / AML / Co-host Podcast “Pláticas de Ciberseguridad” / Tweets are on my own. 🇲🇽
Ivan Castañeda @ivancastl
15K Followers 2K Following 🇲🇽Ingeniero y Maestro en Tecnologías de la Información con conocimientos en OSINT (Open Source Intelligence)
Ignacio Gómez Villas... @ivillasenor
65K Followers 6K Following Periodista | Premio The Merck Foundation (2020) | Coautor «Ópticas de la Corrupción» (2022) y «Desmontar a los Montadeudas» (2023) | Premio AMCS (2025).
Alvaro @alvarombt
19K Followers 915 Following SWE at @Google / @Virustotal. Based in Málaga. Mathematics & Computer Science. Writing about software engineering, AI and security.
A Cyber Guy @USBillAnalyzer
2K Followers 52 Following Opinions are my own. Professional Infosec Researcher and Adversarial AI thinker.
Nick Mykhailyshyn �... @whoareme33
2K Followers 896 Following Security Reseacher and Software Engineer
Pethuraj M @Pethuraj
6K Followers 208 Following Cyber Security Specialist | eWPTXv2 | Security Researcher 👁️⃤ 👨🏻💻 Connect with me on LinkedIn: https://t.co/vnFipcURMo
hasherezade @hasherezade
91K Followers 971 Following Programmer, #malware analyst. Author of #PEbear, #PEsieve, #TinyTracer. Private account. All opinions expressed here are mine only (not of my employer etc)
Myrtus @Myrtus0x0
9K Followers 731 Following Malware Researcher | Developer | @Cryptolaemus1 | @NVIDIA bsky: [email protected]
4ra1n @4ra1n_x
3K Followers 82 Following
ATT&CK @MITREattack
119K Followers 514 Following MITRE ATT&CK® - A knowledge base for describing the behavior of adversaries. Replying/Following/Re-tweeting ≠ endorsement. @ https://t.co/wt46ArkZVt
ExecuteMalware @executemalware
27K Followers 159 Following #malware hunter & analyst. Opinions are my own.
Blue Team News @blueteamsec1
58K Followers 9K Following The cybersecurity home for the latest #BlueTeam, #DFIR, and #ThreatHunting news and tools.
Check Point Research @_CPResearch_
26K Followers 120 Following Fighting cyber threats one research at a time. News from Check Point’s (@checkpointSW) Research team.
Karib0u @bzh_karib0u
363 Followers 2K Following 🇫🇷 CTI Lead - Interested in Malware Analysis, DFIR and powerful OSINT techniques - Tweets are my own
marktsec @marktsec46065
453 Followers 93 Following 💫Cyber Threat Intelligence💫Threat Hunting💫 Malware Analysis 💫OSINT💫Network Security💫
23pds (山哥) @im23pds
16K Followers 6K Following Dad/@SlowMist_Team Partner&CISO/#Web3 Security Researcher/RedTeam/Ai Research #bitcoin
Intarna Co. @intarna_co
1K Followers 0 Following Enterprise threat intelligence platform to monitor cyber incidents, hackers, dark web, vulnerabilities, data leaks and more. For trial access-
fastfire @fastfire
2K Followers 651 Following Head of Cyber Threat Intelligence @ Würth IT, GCTI/CPENT/CEH/CND/CSA/ECSA/ECIH/CTIA, owner of SATAYO CTI platform & deepdarkCTI - member of @Curatedintel
Megatron @TheM3gatr0n
785 Followers 1K Following Just a random cyber guy #ThreatIntelligence | #MalwareAnalysis | #DarkWebResearch | #Geopolitics Student | Views and tweets are my own :)
ANY.RUN @anyrun_app
34K Followers 192 Following Interactive Sandbox & Threat Intelligence trusted by 16K+ SOC & MSSP teams. Triage and respond to phishing & malware faster: https://t.co/DHC75KqDh1
Zhihu Frontier @ZhihuFrontier
12K Followers 196 Following 🚀Bringing China's AI & tech trends, voices and perspectives to the global stage. ⚡️Powered by 知乎/https://t.co/OkIemRZdcj, China's leading knowledge community.
blackorbird @blackorbird
44K Followers 703 Following Peace and Love. Just Analysis/Hunter/Youtuber/AiCoder/Entrepreneur/. #APT #threatIntelligence #Exploit #CTI #meme #cyber #hacker #OSINT #Ai Need Remote Job
Karsten Hahn @struppigel
26K Followers 783 Following MalwareAnalysisForHedgehogs, Principal Malware Researcher at GDATA, he/him 🦔🌈🏳️⚧️
Nolan Kessler @K0DAK22
1K Followers 829 Following Positive Vibes / Innovation / Science / Technology / Psychology / Sports / Meditation / Financial Insight / Exploring Unknown Physics / Open Minds ✨
gündemio @gundemio
2.1M Followers 267 Following Doğru kaynaklardan hızlı haberler sunan yeni nesil sosyal içerik platformu. [email protected]
Searchlight Cyber @SLCyberSec
2K Followers 376 Following Stop threats before they start. Our PTEM platform unifies ASM & dark web intelligence to help defenders prioritize what's exploitable — not just what's exposed.
Tommy M (TheAnalyst) @ffforward
15K Followers 199 Following Threat Researcher @proofpoint | @Cryptolaemus1

ςεяβεяμs - м�... @c3rb3ru5d3d53c
27K Followers 243 Following 💕 Malware Reverse Engineer & Malware Geneticist 💕 #Binlex Developer https://t.co/EKYUS9Itvd 👩💻 She/Her
Intel Owl project @intel_owl
1K Followers 83 Following IntelOwl: analyze files and observables with multiple services and malware analysis tools via a single API at scale #ThreatIntel #OpenSource #SecurityTools
Modat @modat_magnify
2K Followers 58 Following European Internet Intelligence Company. Understand the intent behind internet infrastructure before it is weaponised. Check it out on https://t.co/8w3bQOWmRv
Trends for United States
You might like