Skydev @skydev0h
🍂 💻 🌠 Joined June 2010-
Tweets46
-
Followers122
-
Following100
-
Likes534
Well, performance issues, it’s not uncommon. One out of five...


An SR Summer winner just found a Critical vulnerability, earning him a $25,000 bounty. @skydev0h joined Immunefi in April 2026 and has already earned $44,000 in bounties. He has also been one of the most active users of Immunefi Studio, consistently testing it and sharing
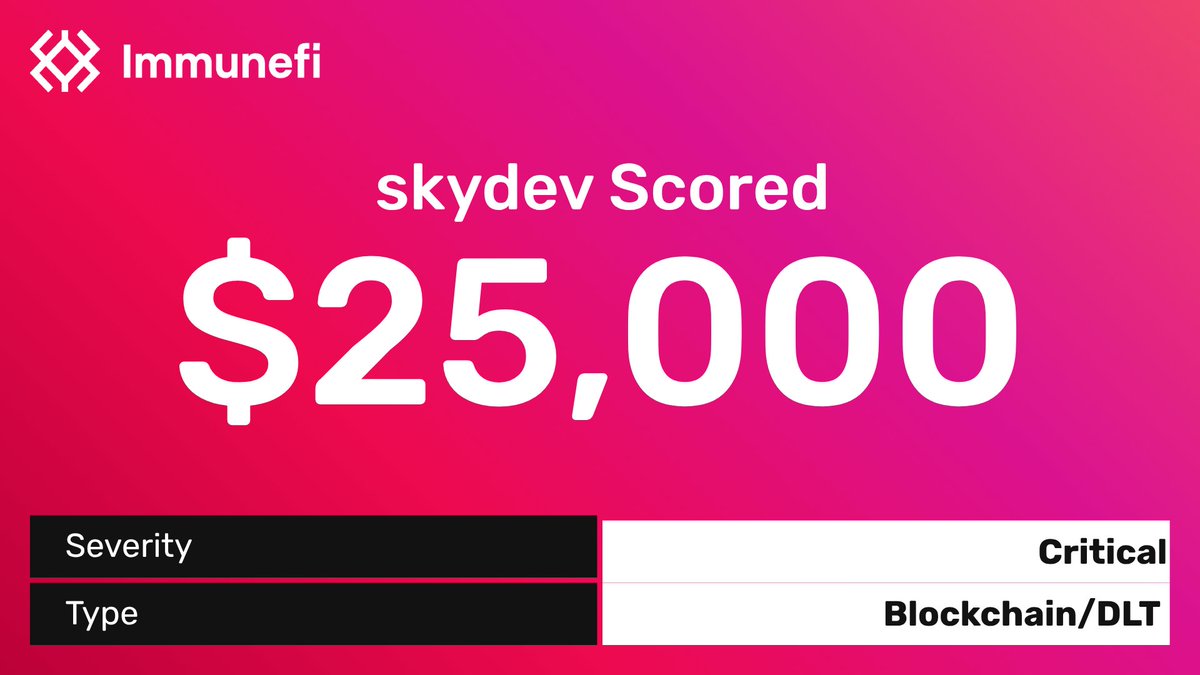
Thanks to you all! 😊 It actually was a bit rough ride, and only this one out of 4 critical reports of the same caliber to this project made it through PKI and duplicates sieve, and there were some reproduction questions, but the project team handled it very professionally (although a bit slowly, but understandable, they were very overloaded) - asked additional questions (rather than closing the report right away like my earlier ones to some other projects), and, ultimately, after presenting a turnkey tool, accepted and rewarded the finding respecting the terms at the time of the submission. Slow, but very pleasant experience, especially if compared to some other projects and platforms. 😔
@tjbecker I think that at some periods of compute starvation their "thinking longer" classifier gets shorter timeout or smaller quant and it is fail closed. Kind of "no time to check this, DENIED" *stamp*
@PeterLynchQuote Now increase temperature to 9001
@Valistheaeth Wow, why I've not seen it earlier... absolutely hate losing ANY data, who tf even thought about setting it just to 30 days by default... thankfully my "Lavos Left Shard" SBC did backups of "Lavos Core" AI zoo station, but something might got lost. Thanks for the important info!
@theBliz_ And they have audacity to call themselves "whitehats". Quite sad that LN does not have a BBP, so that real whitehats would look in their direction as well. Just having a BBP might have resulted in real responsible disclosure and would've avoided all this loss and drama.
@Valistheaeth Always creeps me out. And then anticlimatic "self-subscription" because a new member was added to the project's team. Oh, well.
@ret2basic How to effectively disable bug bounty without delisting it 🙈
@ret2basic @immunefi > - That "paused" program disappeared, pretty much expected Flare? 🙈🙈🙈
What queue, what triaging? Liquid Network did not even have a bug bounty program at the time of incident. If they did more real whitehats would look in their direction >_<
@enisgetmezz @p_tsanev @immunefi Well... yeah. Happens >_<
@v4rvl Yeah, jumped down, and later back up. Hopefully they would give us what we all love as a compensation :)
Finding something on infra is not as difficult as proving it. Unlike SCs where you simply local-fork the chain and demonstrate the vuln, in infra even tens of multi-day experiments may not be enough. Without being able to touch production (obviously) it suddenly may turn out that production environment diverges from local testing one. Nevertheless infra is fun one to play with.
@taimurayaz @NVIDIAAI @NVIDIARTXSpark Very interesting model, although it might be quite noisy. Nevertheless...

@Valistheaeth One critical finding beats a million insights, still 😅
@immunefi Wow, thanks, this one was quite unexpected even for me ☺️
Guess time to brush off the dust here 👀


misbahu @bichistriver
3K Followers 7K Following smart contract hacker | ex @KannAudits | building https://t.co/F85FJxqnMr & @zeta_logistics | marketing @flowdiaryai
Maya @maya_0x01
3 Followers 118 Following Aspiring Smart Contract Security Auditor.🛡️ | Breaking protocols & learning exploits ⚡ | On a mission to find 0-days 🔍 | Open to insights from the OGs 👀
chak pote3 @cadkhoda1
2 Followers 88 Following
Ahmerd Seenerh @SeenerhDev
115 Followers 1K Following Blockchain enthusiant 💻 || Sm@rt C0ntract developer || web3 $3cur!t¥ £ngin33r || farmer🚜 || Machine learning enthusiant 🎰📠 || Front-end developer👩💻 ||

thisvishalsingh 🪐 ... @thisvishalsingh
3K Followers 3K Following securing onchain cryptography next billion dollar (ZKP, MPC, FHE, PQC, TEEs) & making smart contract security accessible to any developer, creator @Zippel_Labs.
Federico Dugaso @FDugaso
5 Followers 184 Following
Joohhnnn @JoohhnnnChase
264 Followers 735 Following @ethereum protocol fellow | prev @Optimism research | I'm glad to discuss any knowledge related to the underlying aspects of Geth and Optimism rollup with you.


Saifu @web3_Saifu
96 Followers 519 Following Smart Contract Security Researching(ongoing)| @CyfrinUpdraft Alumni
kriss_luger @Gunnerdogz
2 Followers 86 Following

Mansi yadav @0xmansiyadav
152 Followers 435 Following Web3 Builder | Hackathon Winner 🏆 Open Source Contributor Exploring Blockchain, AI & Decentralized Systems & GSSOC 25 contributor
سًًَُّّْٕٓ�... @Cachorroexausto
4K Followers 2K Following سًًًًًًًًٌٌٌٌٌٌٌٌٌٌٌٌٍٍٍٍٍٍٍٍٍٍٍََََََََََََََُُُُُُُُُُُُُُُُِِِِِِِِِِِِِِِِِِّّّّّّّّّّْْْْْْْْْْْْْٰٰٰٰٰٰٰٰٰٰٰٰٰٰٰٰٰٰٕٕٕٕٕٕٕٕٕٕٕٕٓٔٓٓٓٓٔٓٓٓٔٓٔٓٔٔٓٔٓٔٔٔٓٔٔٔٔ
Preston Osoro @prestonosoro
137 Followers 668 Following
ChaseTheLight @ChaseTheLight99
2K Followers 800 Following Built LightChaser | 🥇 Bot Racer @code4rena 2024 | 🥇 All-time @glider_xyz | ETHSecurity Badge #150 @thedaofund | Thoughts are my own
Nerdic Guy @g_nerdic
15 Followers 629 Following
amarachi @0_x_0_0_0
854 Followers 3K Following


riptide @0xriptide
10K Followers 4K Following CEO & co-founder @therealgregoai | host of @bountyhunt3rz podcast | top ranked whitehat on @immunefi https://t.co/vWgt74l17W
Sunless @sunless_0x
6 Followers 290 Following
💲𝐂𝐫𝐲𝐩�... @X_cryptographer
1K Followers 407 Following Be Kind, Be Happy, Be Generous ₿- bc1qh7u6am72dag4faavvqfksd5jcful53jjajlzq6


Ramakrishna Kandunuri @RK_SWAERO_KPD
3 Followers 86 Following Technical support engineer L3 | Product support | Software Support Incident management | SAAS | ITIL | CRM- @MERCANS Dubai
flash-a⚡ @flashathehunter
46 Followers 787 Following trash hecker not qualified for anything but trying to be...

CrypteraHQ @CrypteraHQ
42 Followers 243 Following
Anand Vashishtha @AnandVashisht15
961 Followers 2K Following AI + Web3 Builder | Building agentic systems & on-chain apps https://t.co/KyZuv2VHNo https://t.co/x6hYEgxsiT https://t.co/cGdzcfI3uB
ret2basic.eth @ret2basic
3K Followers 4K Following @taichiaudit Founder | Whitehat doing mediations @Immunefi | Core Member @DeFiHackLabs
Oleh PODVYSOTSKYI @OlehPODVYSOTSKI
16 Followers 197 Following
Nosakhare Jesuorobo @CNaj_xyz
84 Followers 259 Following Smartcontracts developer and security researcher || 11x Hackathon winner || Building privacy tooling @fhenix || https://t.co/lE1PiE4IJP
0xkujen @_kujen5
485 Followers 1K Following Senior Penetration Tester at Intrinsic-Security | CARTE | CETP | C-ADPENXv2 | CRTE | CRTP | CARTP | Web3 SR | BB Hunter Personal Blog: https://t.co/JhE466w1U1
Shiva @Neutron975
2K Followers 4K Following paradoxically naive rational optimist • member @superteam • prev @glympsedotfun • DM for work/collab


Mylifechangefast.eth.... @mylifechangefa1
2K Followers 2K Following 21| Banger | Security | Buildoor |Visual Artist | Bussiness alter ego: @realgrew2fast All opinions are my own; no financial advice.
Aviad @Aviad_coh
57 Followers 1K Following “In individuals, insanity is rare; but in groups, parties, nations and epochs, it is the rule. Friedrich Nietzsche
Ihtisham @ihtishamSudo
816 Followers 2K Following Smart Contract Security Researcher | EVM/Solana/Polkadot | 150+ Issues Found | core contributor @SCAuditStudio Portfolio: https://t.co/5KPHOmaszi
" @ProjectStJoan
8 Followers 58 Following The Chinese OSINT to wallet attribution engine. All open source.
@georgibuilds @georgi91757
74 Followers 389 Following From Mechanical Engineer to Smart Contract Security Researcher | EVM
Horvix @Horvix_
10 Followers 797 Following
DeveloperX @DeveloperX_Sec
835 Followers 581 Following Blockchain dev & auditor | Cantina & HackenProof Top 350 All time | ZK | 20+ H/M | 50+ valid findings. Founder @secantpay | building @BIFYOFFICIAL
ten@DGX Spark @tenhkspark
280 Followers 213 Following DGX Spark@4台 LocalLLM 長い異国生活で友達少ないんです。気軽に絡んでください。 債券PM@香港

Joe @joxegr
81 Followers 108 Following
Horvix @Horvix_
10 Followers 797 Following
ret2basic.eth @ret2basic
3K Followers 4K Following @taichiaudit Founder | Whitehat doing mediations @Immunefi | Core Member @DeFiHackLabs
msuiche @msuiche
2K Followers 2K Following hacking since 2002 // AGI-pilled // @tolmohq turning non-deterministic processes into deterministic outcomes.
ten@DGX Spark @tenhkspark
280 Followers 213 Following DGX Spark@4台 LocalLLM 長い異国生活で友達少ないんです。気軽に絡んでください。 債券PM@香港
Essential @only01Essential
3K Followers 110 Following Bug huntoor GoLang | Rust | Move | C++ | Solidity
Joran Honig @joranhonig
6K Followers 1K Following Security Researcher 👨💻 | Professional Bug Bounty Hunter | Resider on the @immunefi leaderboard | On an independent arc
DeveloperX @DeveloperX_Sec
835 Followers 581 Following Blockchain dev & auditor | Cantina & HackenProof Top 350 All time | ZK | 20+ H/M | 50+ valid findings. Founder @secantpay | building @BIFYOFFICIAL
Sameer Ahmad 🇮🇳... @_sameersec
213 Followers 347 Following Bug Hunter. Hacker at @Hacker0x01 @bugcrowd

Vaibhav (VB) Srivasta... @reach_vb
59K Followers 325 Following founder mode @OpenAI | ex @huggingface | F1 fan | *opinions my own
Victor E. Nunez @victornunez
13K Followers 847 Following codex at @OpenAI notes from the frontier dad 🇩🇴 🏀

pashov @pashov
43K Followers 2K Following Security audits @PashovAuditGrp Angel investing @PashovCapital
Bindu Reddy @bindureddy
386K Followers 376 Following CEO of @abacusai - a powerful AI Agent and SuperComputer - Build your company on Abacus AI, ex-AWS & Google
Agontuk @4gontuk
1K Followers 613 Following Security Researcher @cantinaxyz | 5 Crits, 51 Highs, 62 Medium bugs caught | EVM, Solana, ZKproof | Neeloy | DM for private audit
Neo @NeoAIForecast
3K Followers 636 Following Neo Local AI | DGX Spark | Open Models | Agents Open source wins in the end Running LLMs and unnecessary distances. 🏃
Tech2Wild @Tech2Wild
4K Followers 200 Following 🎮 Tech, gaming, AI, and everything in between. 🤖 Building with it, not just talking about it. 🔥 From the mind of @ToNYD2WiLD
Joe @joxegr
81 Followers 108 Following

Mia @MiaAI_lab
31K Followers 391 Following Building with AI & LLMs | Insights, recipes, tools & honest experiments
Miguel Medeiros @_miguelmedeiros
6K Followers 597 Following PGP 46A3AC8395F95A6E6D8F1E34819EDEE4673F3EBB
LonelySloth @lonelysloth_sec
4K Followers 418 Following Animal Intelligence realist. Security Researcher. @Immunefi Elite All Star. https://t.co/p5mT2Ryvtk

Md Ismail Šojal �... @0x0SojalSec
55K Followers 6K Following Cyber_Security_Re-searcher || Ai Re-searcher || AI-Sec|| Malware Analysis II iOS || Pwn || 0SINT || Project AI-StrikeSec || 0ldAccounts Suspended @0xSojalSec ||
0xFrankCastle🦀 @0xcastle_chain
5K Followers 596 Following Rust/Solana Auditor and Security Researcher 🦀 +70 Rust Audits | +60 Solana Audits | +300 criticals/highs Manual + AI audits Dm for Solana Audits | Github👇
thisvishalsingh 🪐 ... @thisvishalsingh
3K Followers 3K Following securing onchain cryptography next billion dollar (ZKP, MPC, FHE, PQC, TEEs) & making smart contract security accessible to any developer, creator @Zippel_Labs.
ControlZ @ControlZ_1337
2K Followers 271 Following @immunefi Elite All Star | Security Researcher @_blockian | #18 all-time whitehat @immunefi | #7 all-time whitehat @hackenproof
Keizo @KeiZo_Zo
248 Followers 148 Following Pentester, Red Teamer, Bug Bounty hobbyist | https://t.co/SZM1N3Q0c1, https://t.co/pf6uqzDPHl
AGTP @AGTPinsights
3K Followers 82 Following Live at 10am ET every Monday and Thursday, hosted by @MichaelWaitze and @RonfortMartin.
fouad @fouadmatin
10K Followers 942 Following @openai cyber preparedness lead // formerly codex, post training, security
Greg Mushen @gregmushen
32K Followers 3K Following Tech veteran turned health hacker. Merging science with self-experimentation to push the limits of longevity and peak performance with age. YRS=50 | N=1.
kernullist @kernullist
1K Followers 3K Following Security and anti-cheat researcher focused on Windows internals. Advancing reliable detection and stronger system integrity. https://t.co/1hoZxnzccW
Kitsune @Kitsuneagentlab
345 Followers 97 Following Hermes + Cyber Security Audit Firm + Systems Engineer Top 300 on Immunefi - SecureHedgehog6828 🏖️ 💻
Siddharth @jeetbhdr
2K Followers 346 Following जैसा मन वैसा संसार It is possible to commit no mistakes and still lose. That is not a weakness; that is life.
しあ @siart_design
1K Followers 91 Following 絵チャとふじすきでお絵描きしてます! 絵チャはMagicalDraw、アプリはPhotoshopとたまにBlenderです。 Illustration/Drawing/Concept Art/VisDev
JanuaryPersimmon2024 @AifosSi
892 Followers 4K Following $224,000+ Web3 earnings | Judge @sherlockdefi | Judge @cantinaxyz | Rust | Solidity | Move Aptos/Sui | Vyper | Golang | CosmosSDK | Cairo | DM for private audit

Abhishek @aacle_
49K Followers 292 Following Building @Vulncure ⚡| Helping founders fix vulnerabilities before hackers find them. Talk to me about: Bug Bounties, LLM Security & React.
Vasko @RoliumGens
1K Followers 1K Following 17 years old jacked ML eng. Road to 1M model downloads!!

Aasif | NoemaLabs @Aasif1552
172 Followers 603 Following Smart Contract Security Researcher | co-founder @NoemaLabs
Vivek @0xvivekd
2K Followers 1K Following Security Researcher I find the bug before it finds the treasury $400M+ exploits prevented #22 Immunefi · #36 HackenProof DMs open for collaborative audits
Kyan @kyan_novoyd
672 Followers 4K Following Security audits @Slot_Zero_Sec @rektoff_xyz @solanaturbine
RobinDesBois 🏹💎 @RobindesboisCT
2K Followers 350 Following Security Researcher on smart contracts Reading charts so you don't have to. | Macro · Crypto · Gold · Oil | Since 2017 🇫🇷 |


You might like